
Configure Versa SASE with JAMF Pro for IOS and MacOS
 For supported software information, click here.
You can onboard Apple devices (macOS and iOS) to your Versa SASE tenant using Jamf Pro. This method uses a property list (.plist) file to ensure consistent, automated deployment.
The Versa SASE agent requires specific configuration parameters to connect to your tenant. Instead of manually entering this information on each device, you can use Jamf Pro to push the configuration parameters in a .plist file. This file acts as a template, pre-populating the agent's required fields and enabling a zero-touch installation for end users. The process is broken down into four main tasks:
- Obtain the configuration parameters
- Create configuration file
- Upload the configuration to Jamf Pro
- Deploy the Versa SASE agent
The following sections describe these tasks in detail.
Obtain the Configuration Parameters
Before you begin in Jamf Pro, you must retrieve information for the configuration parameters from the Versa SASE tenant portal. You can typically find this information in the device onboarding section or agent configuration settings.
The table below shows the configuration parameters that are needed to build the .plist configuration file. The Parameter column lists the keys that represent each parameter in the .plist file, and the Value column shows how the corresponding value should be added to the file. Values should be enclosed in <string> tags, unless otherwise noted.
Some keys use Jamf Pro variables for the values, for example, $JSSID for the device_id key. Jamf Pro automatically replaces these placeholders with device- or user-specific data at deployment time. For other fields, enter the value specific to your environment.
| Parameter | Description | Value |
|---|---|---|
| device_id | Unique hardware identifier | $JSSID or $UUID |
| user_id | User email or identity | |
| device_name | Hostname of the device | $COMPUTERNAME (macOS), $DEVICENAME (iOS) |
| fqdn | Portal fully qualified domain name (FQDN) | Replace with the portal FQDN |
| enterprise_name | Tenant name | Replace with the enterprise name |
| managed_device | Indicates whether the device is managed | Use <true/> or <false/> tag |
| log-level | Set the log level via MDM. | Enter one of the following: Info, Debug, Error, Warning, or Verbose |
| default_browser | Enables the default browser for authentication | Use <true/> or <false/> tag |
| is_versa_root_ca_required | Honors the Versa root certificate. Set to false to use a customer certificate. | Use <true/> or <false/> tag |
| skip_onboarding_screens | Skips the onboarding screens on first launch | Use <true/> or <false/> tag |
| Parameters introduced in version 7.7.1 (macOS only) | ||
| ekuid | Enables extended key usage (EKU) identifier-based certificate selection | Use <true/> or <false/> tag |
| eku_id_devicecert | EKU object identifier (OID) for device certificate authentication | Example: 1.3.6.1.4.1.12345.21 |
| eku_id_usercert | EKU OID for user certificate authentication | Example: 1.3.6.1.4.1.12345.20 |
| fetch_username_from_certificate | Fetches the username from the client certificate | Use <true/> or <false/> tag |
| username_field | Certificate field to use as the username (CN or SAN) | Enter CN or SAN |
| cert_issuer | Certificate issuer name | Example: CN=ROOT CA2 Intermediate CA1 |
| Parameters introduced in version 7.7.3 (macOS only) | ||
| fail_close_allowed_ips | IP addresses or subnets allowed through the firewall in fail-close state | Example: 192.168.1.0/24, 10.0.0.1 |
| disable_dns_proxy | Set to true to skip DNS proxy activation. Set to false to enable the normal DNS proxy activation flow. | Use <true/> or <false/> tag |
Create the Configuration File
You create the configuration file for the Versa SASE agent as .plist file. The .plist file contains key-value pairs that define the configuration. Each configuration parameter is represented by a key. For each key, you provide a value based on the information obtained in Obtain the Configuration Parameters, above.
For some of the values, you use Jamf Pro variables. These are placeholders that Jamf Pro automatically resolves to the correct device or user data at deployment time. For example, for the device_id key, you use the $JSSID variable for the value.
Create a PLIST File
Create a file that contains the key-value pairs for your configuration. Use a plain text editor or a dedicated .plist editor to create this file. Save it with a .plist extension (for example, versa_sase_config.plist).
For each configuration parameter, enter a key and corresponding value, as shown in the example below. Replace the variables with values with your actual environment.
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>device_id</key>
    <string>$JSSID</string>
    <key>device_name</key>
    <string>$COMPUTERNAME</string>
    <key>user_id</key>
    <string>$EMAIL</string>
    <key>fqdn</key>
    <string><your-portal-fqdn></string>
    <key>enterprise_name</key>
    <string><your-enterprise-name></string>
    <key>managed_device</key>
    <true/>
    <key>default_browser</key>
    <false/>
    <key>is_versa_root_ca_required</key>
    <false/>
    <key>skip_onboarding_screens</key>
    <true/>
    <key>disable_dns_proxy</key>
    <false/>
    <key>log_level</key>
    <string>Verbose</string>
    <key>fail_close_allowed_ips</key>
    <array>
        <string>192.124.249.120/32</string>
    </array>
</dict>
</plist>
For more information about variables used by Jamf Pro, see the Jamf Pro documentation.
Upload the Configuration to Jamf Pro
After you define the configuration in the .plist file, you upload the .plist file to Jamf Pro for MDM. The upload process differs depending on whether the settings apply to application behavior (app configuration) or system-level preferences (custom configuration). When onboarding the Versa SASE agent, you typically need to do both.
To upload the .plist file for app configuration:
- Log in to your Jamf Pro console.
- Navigate to Computers > Configuration Profiles (for macOS) or Mobile Devices > Configuration Profiles (for iOS).
- Click + New to create a new profile.
- Enter a Name for the profile, for example "Versa SASE Agent Configuration".

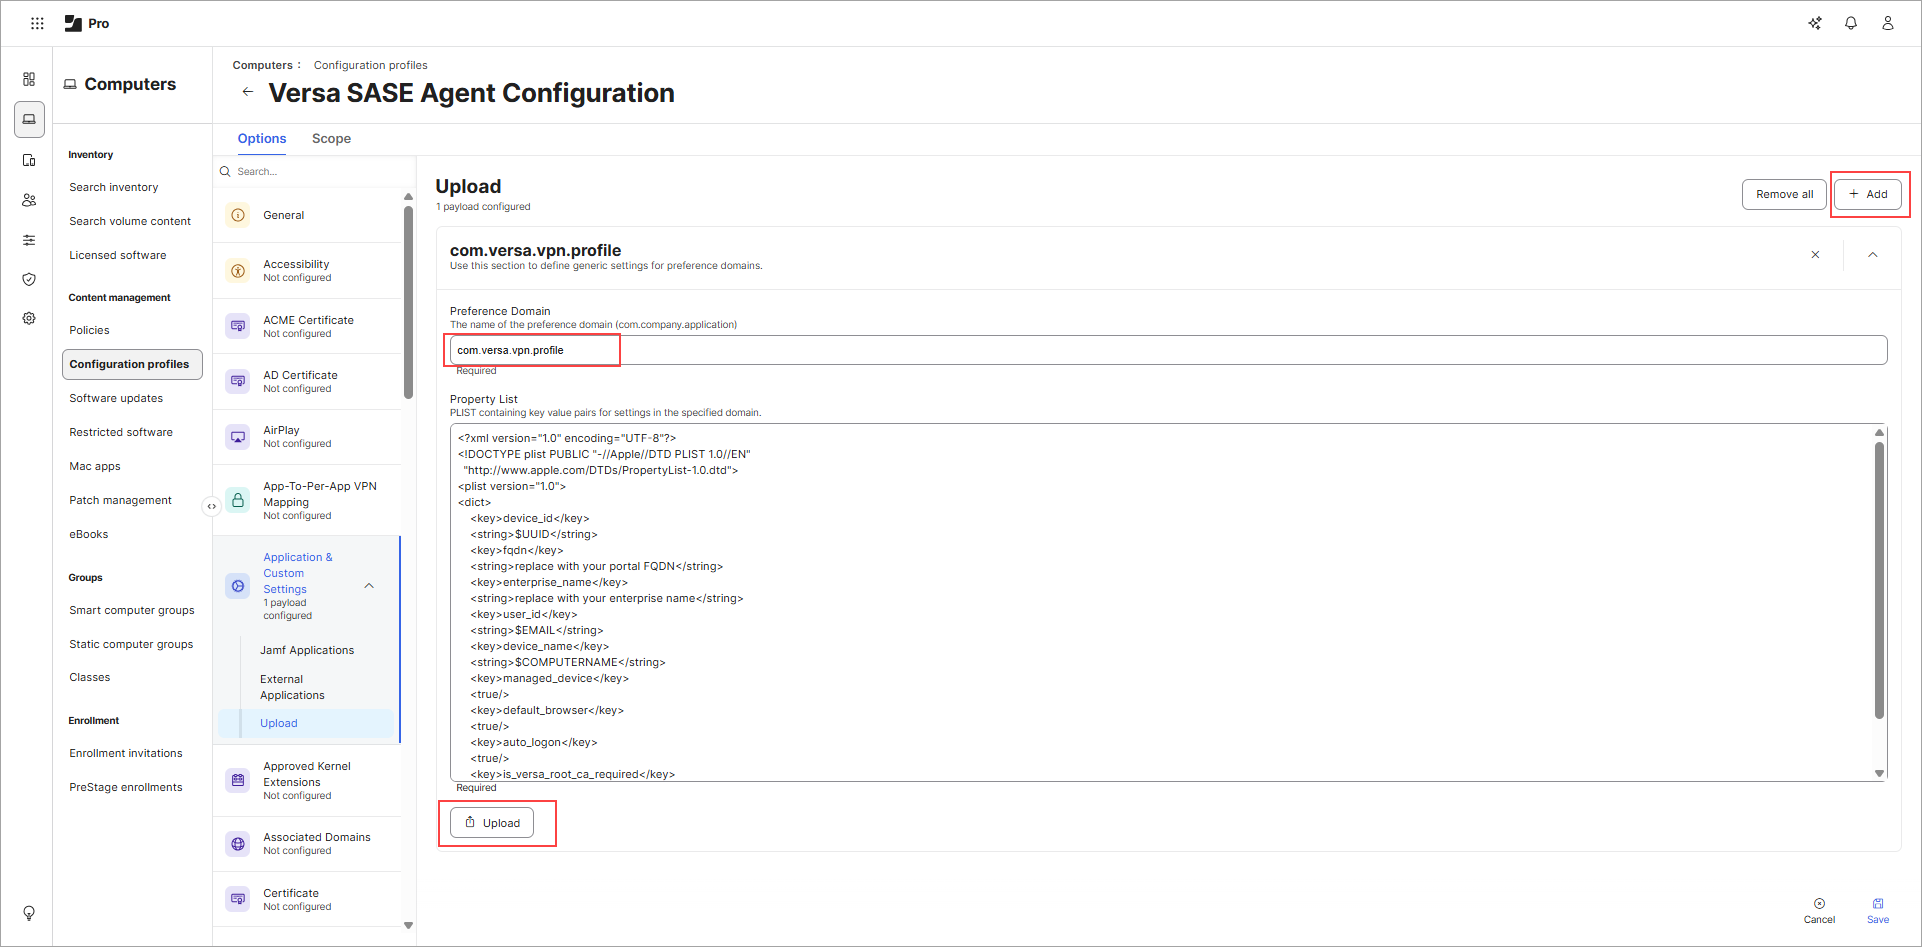
- In the left-hand menu, select Application & Custom Settings, and then select Upload.
- Click + Add
- In the Preference Domain field, enter com.versa.vpn.profile
- Click Upload.
- Upload the .plist file you created in the Create the .plist File section, above.
- In the left menu, select Notifications.
- Click + Add, and then enter information for the following fields:
Field Description App Name Enter the application name. Bundle ID Enter the bundle ID for the platform:
- macOS—com.versa.systemextension
- iOS—com.versa.saseclientcatalyst
Note: Repeat this step for each bundle ID. You must enable notifications for each bundle ID separately.

- In the left menu, select System Extensions (this step applies to macOS only).
- Configure the system extension with the following values:
Field Description System extension types Select Non-removable system extensions from the UI. Team identifier Enter the following value: 47J4JTFE29 Bundle ID Enter the following value: com.versa.systemextension.sslse. - Click + Add and then enter the Bundle ID.

- In the left menu, select VPN.
- Click Configure.
- Configure the following values:
Field MacOS IOS Connection type Select Custom SSL Custom SSL Identifier Enter com.versa.systemextension com.versa.saseclientcatalyst Server Enter your Versa gateway FQDN. For example, acme.poc.versanow.net. Enter your Versa gateway FQDN. For example, acme.poc.versanow.net. Provider bundle identifier Enter com.versa.systemextension Enter com.versa.saseclientcatalyst Provider type Packet tunnel Packet tunnel

- Click Save.
Deploy the Versa SASE Client
After you upload the configuration parameters, you must deploy the Versa SASE application separately.
To deploy the Versa SASE macOS client, you do the following:
- Upload the Versa SASE application package
- Create a Jamf policy
- Enroll macOS devices
The following sections describe these tasks in detail.
Upload the Versa SASE Package
Before you create a policy or configuration profiles, upload the Versa SASE package to Jamf Pro.
- In Jamf Pro, click Settings > Computer Management > Packages.
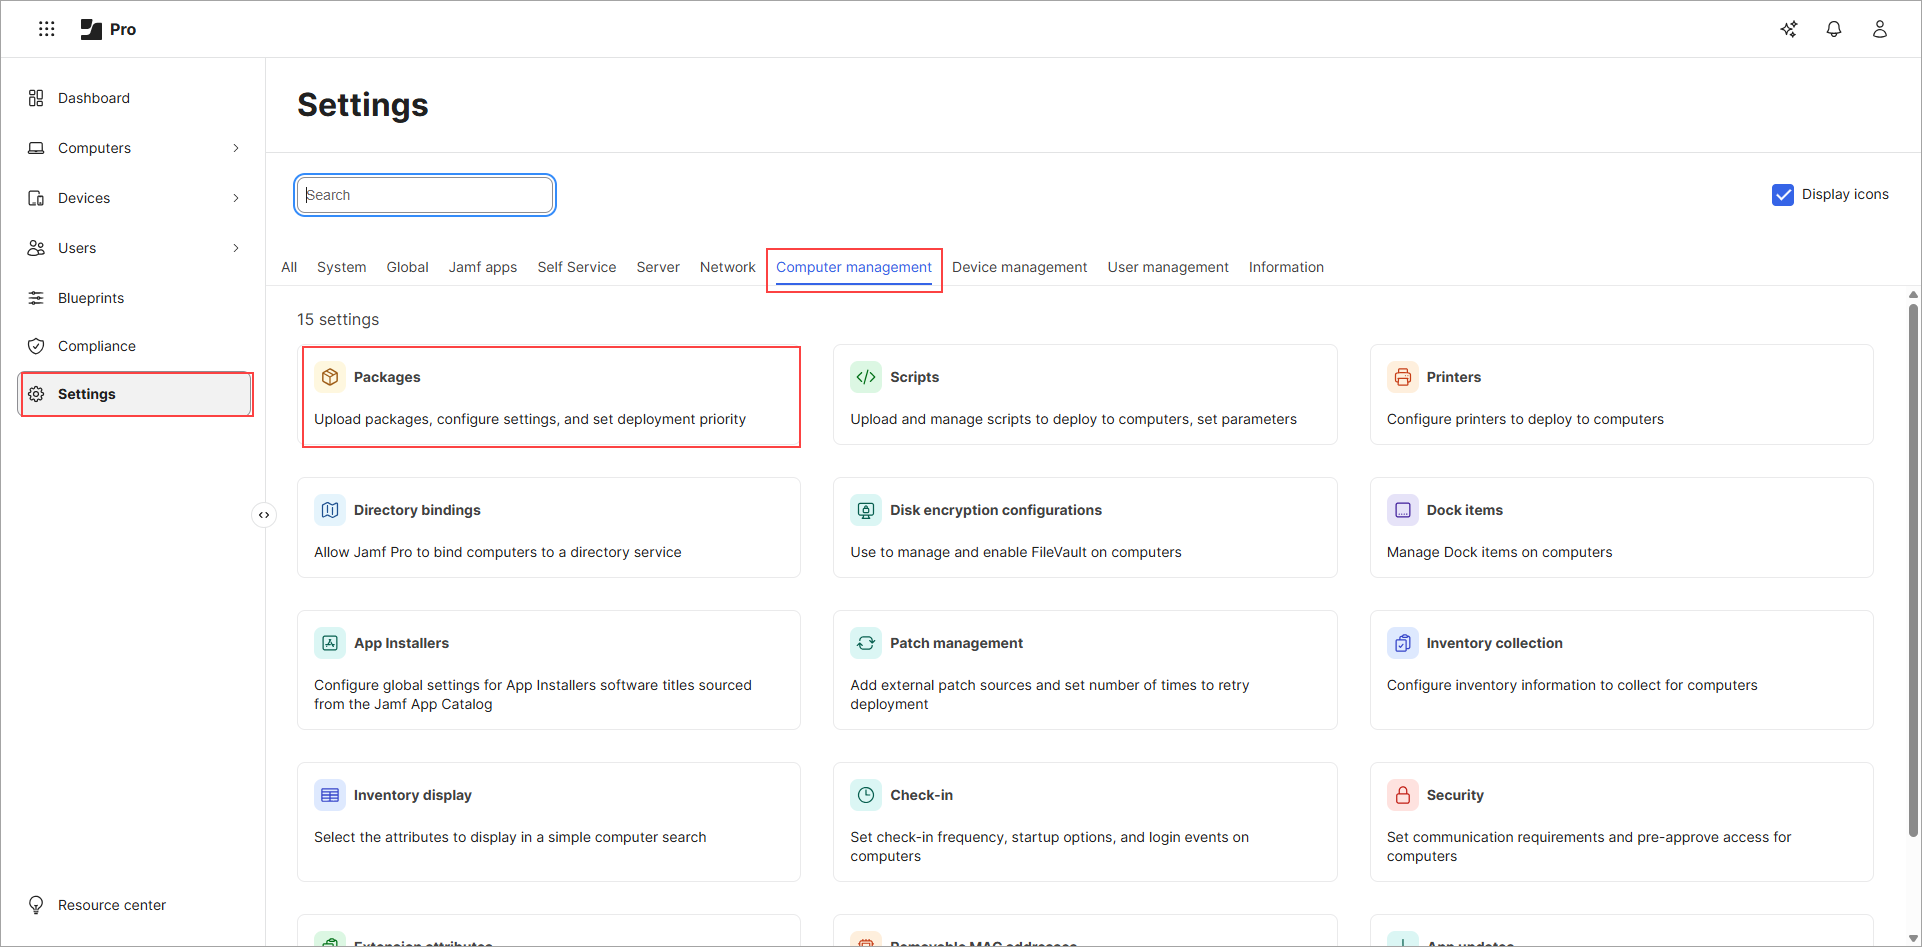
- Click + New.
- Click Upload.
- Enter a display name for the package.
- Upload the Versa SASE macOS package.

- Click Save.
Create a Policy
To install the Versa SASE package on target devices, you must create a policy in Jamf Pro.
- In Jamf Pro console, navigate to Computers > Policies.
- Click + New.
- Under General, configure the following fields:
Field Description Display name Enter a descriptive name for the policy Trigger Select the trigger — for example, Login or Recurring Check-in Execution frequency Select the required frequency

- In the left menu, select Packages.
- Click Configure.
- Click Add in the corresponding row to the Versa SASE package you uploaded.
- Click Scope.
- Click + Add, and then select the target devices or groups.

- Click Save.
Enroll MacOS Devices
Enable Enrollment
To allow users to enroll their devices, enable user-initiated enrollment in Jamf Pro:
- In your Jamf Pro Pro console, click Settings > Global > User-Initiated Enrollment.
- Verify that enrollment is enabled.
Enroll the Device
To enroll your device, open your JAMF enrollment URL, for example, https://versa.jamfcloud.com, and complete the following steps:
- Open https://<your-jamf-url>/enroll in a browser.
- Log in with corporate credentials.
- Click Enroll.
- Install the MDM profile in System Settings.
- Click Approve to approve management.
Verify Enrollment
To confirm a device is enrolled, click Computers > Search Inventory and then search for the device. The enrolled macOS device displays in the inventory.
Post-Deployment Behavior (v7.7.0) (MacOS)
After deployment and first launch, the following permissions are automatically approved with MDM:
- Registration
- Notifications
- Network extension
- System extension
The following permissions require manual user approval:
- Allow local networks
- Allow location services
IOS-Specific Deployment
This section covers steps specific to deploying the Versa SASE client on iPhone and iPad devices through Jamf Pro.
Create a Configuration Profile (IOS)
- Navigate to Devices > Configuration Profiles > New.

- Under the General section, enter information for the following fields:

Field Description Display Name Enter a descriptive name. Level Set to Device Level. Distribution Method Select Install Automatically or Make Available in Self Service. - Click Save.
Configure Notifications for the Versa SASE Client
- Navigate to Devices > Notifications > +Add.
- In the App Name field, enter Versa SASE Client.
- Select Versa SASE Client. The Bundle ID field populates automatically.
- Choose whether to Enable or Disable notifications:
- Enable—Users see the "Allow/Don't Allow Notifications" prompt after installation.
- Disable—Users do not see this prompt after installation.

- Click Save.
Note: Notification pre-configuration works only on supervised devices.
Configure IOS VPN Profile
Add or modify VPN settings within your configuration profile as follows:
- Search for VPN in the payload search box.
- Click the VPN payload to open its settings.
- Configure the following fields:
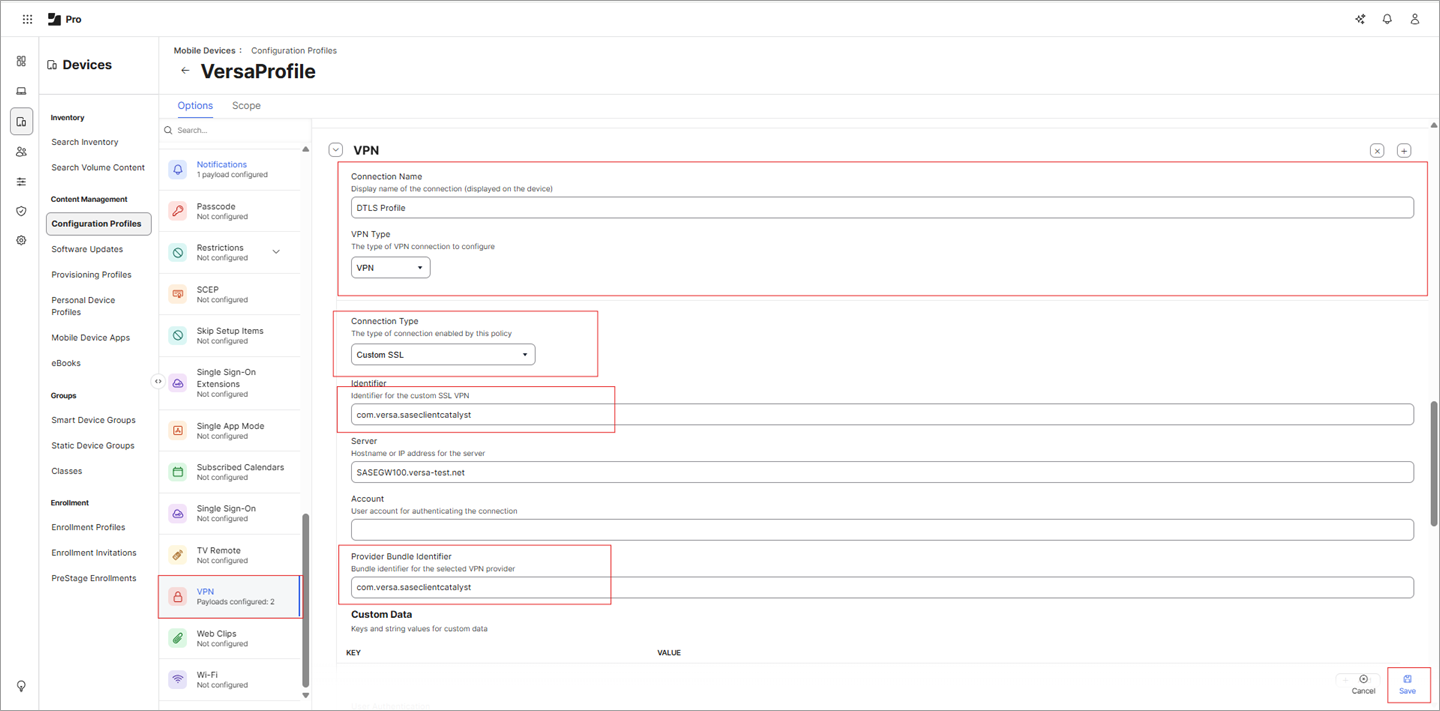
Field Description Connection Name Enter the name displayed in VPN settings on the device. VPN Type Select VPN (for DTLS). Connection Type Select SSL. Identifier Enter the following value: com.versa.saseclientcatalyst Server Enter your Versa gateway FQDN. For example, acme.poc.versanow.net. Provider Bundle Identifier Enter the following value: com.versa.saseclientcatalyst - Click Save.
Deploy IOS App (App Store or In-House .ipa)
IOS apps must be added from the Mobile Device Apps section in Jamf Pro.
- Navigate to Mobile Device Apps > New.

- Select the app source:
- App Store App—Search for "Versa SASE Client." Click Add. The app name, version, and bundle identifier are populated automatically.

- In-House App—Upload the .ipa file.
- App Store App—Search for "Versa SASE Client." Click Add. The app name, version, and bundle identifier are populated automatically.
- Set the Distribution Method to Install Automatically / Prompt Users to Install.

- Optionally, enable Remove app when MDM profile is removed.
- Click the Scope tab and select the target devices, groups, or users.

- In the App Configuration section, add the following plist XML:

<dict> <key>device_id</key> <string>$UUID</string> <key>fqdn</key> <string>replace with your portal FQDN</string> <key>enterprise_name</key> <string>replace with your enterprise name</string> <key>user_id</key> <string>$EMAIL</string> <key>device_name</key> <string>$DEVICENAME</string> <key>managed_device</key> <true/> <key>default_browser</key> <true/> <key>is_versa_root_ca_required</key> <true/> </dict> - Click Save. The application is pushed to the specified users and devices. Users receive an install prompt on their device.

- Tap Install.
IOS Enrollment Methods
Before uploading or assigning the application, you must enroll devices in Jamf Pro. The following table describes the available enrollment methods:
| Method | Best For | Description |
|---|---|---|
| Automated Device Enrollment (ADE) | Organization-owned devices | Uses Apple Business Manager (ABM) or Apple School Manager (ASM). Devices are automatically enrolled when powered on and connected to the internet. |
| User-Initiated Enrollment | Smaller setups or testing | Users manually enroll by visiting a Jamf enrollment URL in Safari on their iOS device. See User-Initiated Enrollment (IOS), below. |
| Account-Driven User Enrollment | BYOD scenarios | Users enroll personal devices using a discovery URL and their managed Apple ID. Provides limited management to protect user privacy. |
User-Initiated Enrollment (IOS)
- To prepare Jamf Pro, log into Jamf Pro and configure your enrollment settings. Ensure you have a valid SSL certificate for secure communication.
- Get the Enrollment URL (typically https://<your-jamf-server-url>/enroll). Share this link with users.
- Enroll the Device:
- On the iOS device, open Safari and go to the enrollment URL.
- Log in with the user's Jamf Pro credentials.
- Follow prompts to install the MDM profile.
- Accept the profile installation in Settings > General > Profiles.
- Device Management Begins — once enrolled, the device reports inventory data to Jamf Pro, and IT can push apps, configurations, and policies.
For more information, see the Jamf Pro documentation.
Post-Deployment Behavior (v7.7.0) (IOS)
After deployment and launching the app, the following permissions are automatically approved through MDM:
- Registration
- Notifications—This prompt is skipped if Notifications are pre-configured in the configuration profile; applicable only to supervised devices.
- Allow VPN—This prompt is skipped if VPN settings are already defined in the configuration profile.
- Allow Local Networks—This prompt can be avoided if the device name is specified in the plist file (use $DEVICENAME for the device_name key).
The following permission still requires manual user approval:
- Allow Location Services
DTLS Profile Behavior on IOS
In DTLS-based SSL VPN profiles on iPhone and iPad, the On Demand option does not appear. This means users cannot manually enable or disable On Demand from the VPN settings. This is expected behavior for DTLS profiles on iOS.
Verification
After the deployment policies have run, verify that the onboarding is successful:
- In Jamf Pro—Check the device's history to confirm the policy and profile were applied successfully.
- On the device—Users can confirm the agent is running and connected by checking its status (for example, in the macOS menu bar).
- In the Versa SASE Tenant Portal—Navigate to your View > Secure Access list. The newly onboarded devices should appear and show a connected or online status.
Managed App Configuration for In-House Apps Developed with Jamf Certificate SDK
In-house apps built with the Jamf Certificate SDK rely on managed app configuration to communicate with Jamf Pro and AD CS. Each key-value pair supplies a specific piece of information, from identifying the device to specifying the certificate template, that Jamf Pro uses to authenticate the request and issue the correct certificate.
All values are of type String unless noted otherwise. Many values support Jamf Pro variable substitution, for example, $SERIALNUMBER, so that certificates can be personalized per device without manual configuration.
This reference article describes the required managed application configuration key-value pairs for iOS and iPadOS in-house applications that use the Jamf Certificate SDK to request certificates from Active Directory Certificate Services (AD CS) through Jamf Pro.
Note: Configure these key-value pairs in the App Configuration section of the managed application record in Jamf Pro before deploying the application to devices.
Key-Value Pairs
The following table lists every key-value pair required for in-house apps that integrate with the Jamf Certificate SDK. All keys are case-sensitive.
| Key | Value | Type | Description |
|---|---|---|---|
| com.jamf.config.jamfpro.invitation | $MOBILEDEVICEAPPINVITE | String | A unique token that verifies the MDM server matches the specified Jamf Pro instance. Jamf Pro replaces the variable at deployment time. |
| com.jamf.config.device.udid | $MANAGEMENTID (Jamf Pro 11.5.1 and later) $UDID (Jamf Pro 11.5.0 and earlier) |
String | The device identifier used to confirm which device is requesting the certificate. Use $MANAGEMENTID for environments that support account-driven enrollment; use $UDID for earlier Jamf Pro versions. |
| com.jamf.config.jamfpro.url | https://<jamf_pro_server_url>/ | String | The fully qualified Jamf Pro server URL. Must include the correct protocol (https://), the fully qualified domain name (FQDN), and the port number if your server uses a non-standard port. Enter the literal URL — variable substitution is not supported for this key. |
| com.jamf.config.certificate-request.pkiId | Organization-specific PKI ID | String | Identifies the AD CS instance (PKI connector) that should process the certificate request. Obtain this value from your Jamf Pro administrator or AD CS configuration. |
| com.jamf.config.certificate-request.template | Template name (for example, Machine or User) | String | Specifies the certificate template to use when generating the certificate. The template name must match the name configured in AD CS exactly. |
| com.jamf.config.certificate-request.subject | X.500 name format (for example, cn=$SERIALNUMBER) | String | The subject of the certificate in X.500 distinguished name format. Supports Jamf Pro variable substitution, enabling dynamic per-device or per-user values. Common variables include $SERIALNUMBER, $USERNAME, and $DEVICENAME. |
| com.jamf.config.certificate-request.sanType | SAN type (for example, rfc822Name or dNSName) | String | Specifies the type of Subject Alternative Name (SAN) to include in the certificate. The value must be a valid SAN type recognized by AD CS. |
| com.jamf.config.certificate-request.sanValue | SAN value (supports variable substitution) | String | The value for the Subject Alternative Name specified in sanType. Supports Jamf Pro variable substitution so that the SAN can be tailored per device or user at deployment time. |
| com.jamf.config.certificate-request.signature | $JAMF_SIGNATURE_com.jamf.config.certificate-request | String | A cryptographic signature generated by Jamf Pro that protects the certificate request from tampering. Jamf Pro validates this signature before issuing the certificate. Always use the exact variable token shown — do not enter a literal value. |
Note: The com.jamf.config.certificate-request.signature key must be present and must use the exact variable token $JAMF_SIGNATURE_com.jamf.config.certificate-request. If this key is missing or the signature is invalid, Jamf Pro will reject the certificate request.
Jamf Pro Variable Substitution
Several key values support Jamf Pro's variable substitution feature. When the app configuration is deployed to a device, Jamf Pro automatically replaces each variable token with the real value for that specific device or user. The following variables are commonly used in certificate configurations:
- $MOBILEDEVICEAPPINVITE—App invitation token unique to the device and app.
- $MANAGEMENTID—Device management identifier (Jamf Pro 11.5.1 and later; supports account-driven enrollment).
- $UDID—Device UDID (Jamf Pro 11.5.0 and earlier).
- $SERIALNUMBER—Device serial number.
- $USERNAME—Username of the user assigned to the device in Jamf Pro.
- $DEVICENAME—Name of the device as recorded in Jamf Pro.
- $JAMF_SIGNATURE_com.jamf.config.certificate-request—Cryptographic signature for the certificate request payload.
Device Identifiers
The device key (com.jamf.config.device.udid) accepts two different variable tokens depending on your Jamf Pro version:
- Jamf Pro 11.5.1 and later—Use $MANAGEMENTID. This token supports both account-driven enrollment and device enrollment, making it the preferred identifier going forward.
- Jamf Pro 11.5.0 and earlier—Use $UDID. This token provides the hardware UDID of the device.
Note: Using $MANAGEMENTID on older Jamf Pro versions, or $UDID on newer versions where account-driven enrollment is in use, may result in certificate request failures.
Jamf Pro Server URL Identifier
The value for com.jamf.config.jamfpro.url must be the complete URL of your Jamf Pro server. Include all of the following elements:
- Protocol—Always https://.
- Fully Qualified Domain Name (FQDN)—For example, jamfpro.example.com.
- Port—Include the port if your server uses a non-standard port (for example, :8443). Omit the port if your server uses the standard HTTPS port 443.
- Trailing slash—Append a trailing / at the end of the URL.
Example: https://jamfpro.example.com:8443/
Certificate Request Signature
The signature key-value pair provides a security layer that prevents unauthorized modification of the certificate request. The workflow is as follows:
- When the managed app configuration is deployed, Jamf Pro generates a cryptographic signature over the certificate request fields.
- The signature is injected into the app configuration using the variable token $JAMF_SIGNATURE_com.jamf.config.certificate-request.
- When the in-house app submits a certificate request, Jamf Pro verifies the signature before forwarding the request to AD CS.
- If the signature is missing or does not match, Jamf Pro rejects the request and no certificate is issued.
Note: The signing and verification process is handled entirely by Jamf Pro. You do not need to generate or manage the signature manually.
Supported Software Information
SASE Client releases 7.6.7 and later support all parameters described in this article, except:
- Release 7.7.1 introduces the macOS parameters listed under Parameters introduced in version 7.7.1 (macOS Only).
- Release 7.7.3 introduces the macOS parameters listed under Parameters introduced in version 7.7.3 (macOS Only).