
Configure Versa SASE with Ivanti for IOS and MacOS
 For supported software information, click here.
You can onboard Apple devices (macOS and iOS) to your Versa SASE tenant using Ivanti Neurons. This method uses a property list (.plist) configuration file to ensure consistent, automated deployment.
The Versa SASE agent requires specific configuration parameters to connect to your tenant. Instead of manually entering this information on each device, you can use Ivanti to push the configuration parameters in a .plist file. This file acts as a template, prepopulating the necessary fields for the agent and ensuring a zero-touch installation for end users. The process is broken down into four main tasks:
- Obtain the configuration parameters
- Create the configuration file
- Upload the configuration to Ivanti
- Deploy the Versa SASE agent
The following sections describe these tasks in detail.
Obtain the Configuration Parameters
Before you begin in Ivanti, you must retrieve information for the configuration parameters from the Versa SASE tenant portal. You can typically find this information in the device onboarding section or agent configuration settings.
The table below shows the configuration parameters that are needed to build the .plist configuration file. The Parameter column lists the keys that represent each parameter in the .plist file, and the Value column shows how the corresponding value should be added to the file. Values should be enclosed in <string> tags, unless otherwise noted.
Some keys use Ivanti macros for the values, for example, ${deviceGUID} for the device_id key. Ivanti automatically replaces these placeholders with device- or user-specific data at deployment time. For other fields, enter the value specific to your environment.
| Parameter | Description | Value |
|---|---|---|
| device_id | Unique hardware identifier | ${deviceGUID} (Ivanti macro) |
| user_id | User email or identity | ${userEmailAddress} (Ivanti macro) |
| device_name | Hostname of the device | ${deviceName} (Ivanti macro) |
| fqdn | Portal fully qualified domain name (FQDN) | Replace with the portal FQDN |
| enterprise_name | Tenant name | Replace with the enterprise name |
| managed_device | Indicates whether the device is managed | Use <true/> or <false/> tag |
| log-level | Set the log level via MDM. | Enter one of the following: Info, Debug, Error, Warning, or Verbose |
| default_browser | Enables the default browser for authentication | Use <true/> or <false/> tag |
| is_versa_root_ca_required | Honors the Versa root certificate. Set to false to use a customer certificate. | Use <true/> or <false/> tag |
| skip_onboarding_screens | Skips the onboarding screens on first launch | Use <true/> or <false/> tag |
| Parameters introduced in version 7.7.1 (macOS only) | ||
| ekuid | Enables extended key usage (EKU) identifier-based certificate selection | Use <true/> or <false/> tag |
| eku_id_devicecert | EKU object identifier (OID) for device certificate authentication | Example: 1.3.6.1.4.1.12345.21 |
| eku_id_usercert | EKU OID for user certificate authentication | Example: 1.3.6.1.4.1.12345.20 |
| fetch_username_from_certificate | Fetches the username from the client certificate | Use <true/> or <false/> tag |
| username_field | Certificate field to use as the username (CN or SAN) | Enter CN or SAN |
| cert_issuer | Certificate issuer name | Example: CN=ROOT CA2 Intermediate CA1 |
| Parameters introduced in version 7.7.3 (macOS only) | ||
| fail_close_allowed_ips | IP addresses or subnets allowed through the firewall in fail-close state | Example: 192.168.1.0/24, 10.0.0.1 |
| disable_dns_proxy | Set to true to skip DNS proxy activation. Set to false to enable the normal DNS proxy activation flow. | Use <true/> or <false/> tag |
Create the Configuration File
You create the configuration file for the Versa SASE agent as .plist file. The .plist file contains key-value pairs that define the configuration. Each configuration parameter is represented by a key. For each key, you provide a value based on the information obtained in Obtain the Configuration Parameters, above.
For some of the values, you use Ivanti macros. These are placeholders that Ivanti automatically resolves to the correct device or user data at deployment time. For example, for the device_id key, you use the ${deviceGUID} macro for the value.
Note: For iOS, creating a .plist file is not required. Instead of uploading a file, you can manually enter the key-value pairs directly in the Ivanti interface. See Upload a PLIST File for App Configuration (IOS), below.
Create a PLIST File
Create a file that contains the key-value pairs for your configuration. Use a plain text editor or a dedicated .plist editor to create this file. Save it with a .plist extension (for example, versa_sase_config.plist).
For each configuration parameter, enter a key and corresponding value, as shown in the example below. Replace the variables with values with your actual environment.
XML
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
        <key>device_id</key>
        <string>${deviceGUID}</string>
        <key>fqdn</key>
        <string>replace with your portal FQDN</string>
        <key>enterprise_name</key>
        <string>replace with your enterprise name</string>
        <key>user_id</key>
        <string>${userEmailAddress}</string>
        <key>device_name</key>
        <string>${deviceName}</string>
        <key>managed_device</key>
        <true/>
        <key>default_browser</key>
        <false/>
        <key>is_versa_root_ca_required</key>
        <true/>
        <key>skip_onboarding_screens</key>
        <false/>
        <key>auto_logon</key>
        <true/>
        <key>fetch_username_from_certificate</key>
        <false/>
        <key>ekuid</key>
        <true/>
        <key>eku_id_devicecert</key>
        <string>{EKU Authentication ID to be matched}</string>
        <key>eku_id_usercert</key>
        <string>{EKU Authentication ID to be matched}</string>
</dict>
</plist>
Upload the Configuration to Ivanti
After you define the configuration in the .plist file, you upload the .plist file to Ivanti Neurons for MDM. The upload process differs depending on whether the settings apply to application behavior (app configuration) or system-level preferences (custom configuration). When onboarding the Versa SASE agent, you typically need to do both.
Upload a PLIST File for App Configuration (IOS)
Use app configuration for user-specific parameters, such as email address and tenant name, so the app is pre-configured when it launches.
Note: For iOS, Ivanti provides a UI to input keys directly. Instead of uploading a .plist file, you can use the Add+ option in Apple Managed App Configuration to enter each key-value pair manually. You can use the following procedure for both methods.
To upload the .plist file for app configuration:
- In Ivanti Neurons for MDM, click Apps > App Catalog.
- Select the Versa SASE application (for iOS platform).
- Click the App Configurations tab.
- In the Apple Managed App Configuration section, click the + icon.

- Enter a Name for the Configuration Setup.
- In the Apple Managed App Settings section, upload the configuration using one of the following methods:
- To upload a .plist file, click Use .plist. Ivanti parses the file and displays the keys in a table.
- To manually enter each key-value pair, click + Add. For a full list of keys, see Obtain the Configuration Parameters.

- In Distribute this App Config, select one of the following options: Everyone with App, No One, or Custom.
- Click Save.
Upload a PLIST File for System Preferences (MacOS Custom Profile)
The following steps allow you to push the .plist file to the /Library/Preferences folder on the device. Use this configuration type for system-wide settings or extensions.
To upload a .plist file for system preferences:
- In Ivanti Neurons for MDM, click Configurations > + Add.
- Search for and select Custom.
- In the Name field, enter macOS – Versa System Prefs.
- Under Choose OS, select macOS.
- In the Configuration Setup section, click Choose File and then upload your .plist file.

- Click Next.
- In step 2, Distribute, click the Enable this Configuration checkbox.
- Select the appropriate channel for who the configuration applies to:
- Device Channel—Applies the profile at the system level, before any user logs in. Recommended for system extensions and VPN profiles.
- User Channel—Applies the profile per logged-in user.

- Choose one of the following options to define distribution:
- All Devices
- No Devices
- Custom
- Click Done.
Deploy the Versa SASE Agent
After you upload the configuration parameters, you must deploy the Versa SASE agent application separately.
To deploy the Versa SASE macOS client, you do the following:
- Upload the Versa SASE application package
- Configure VPN
- Approve system extensions
- Configure application notifications
- Enroll macOS devices
Upload the Versa SASE Application Package
- Log in to your Ivanti Neurons for MDM console.
- Select Apps > App Catalog.
- Click + Add.
- Select In-House as the app type.
- Drag and drop the Versa SASE .pkg file.

- Click Next.
- In the Package Apps section, select com.versa.systemextension as the primary application.

- Click Next.
- In step 3, Add Screenshots, you can upload images to add screenshots, or you can skip this step.

- Click Next.
- In step 4, Delegate, select Do not delegate this app.

- Click Next.
- In step 5, Distribute, select a distribution group.

- Click Next.
- In step 6, Configure, click the + icon next to Install on device.

- In the Configuration Setup page, enter the following information:
Field Description Name Enter the following value: Install Application configuration settings. Description (Optional) Click + Add to enter a description. This allows specifying install settings for an application. Device Installation Configurations Click the toggle to the On position, and then select Require installation on device. Set App Install Priority Select High.

- In Distribute this App Config section, select the same group used in step 5, Distribute.
- Click Done.
Configure VPN (Silent VPN Adapter)
A silent VPN adapter establishes a VPN tunnel in the background without requiring user interaction or approval prompts. The Versa SASE system extension functions as a packet tunnel provider, which macOS registers as a network interface and manages automatically.
To configure a packet tunnel provider for the Versa SASE system extension, you must use a Custom VPN setup in Ivanti Neurons for MDM. Use the provider bundle identifier com.versa.systemextension to support both SSL and IPsec-based tunnels. This ensures macOS treats the extension as a network interface.
Create Custom VPN Configuration
- In Ivanti Neurons for MDM, click Configurations, and then click + Add.
- Search for and select VPN.
- In the Configuration Setup section, enter the following information:
Field Description Name Enter the following value: Versa SASE - VPN Configuration. Connection Type Select Custom SSL. Identifier Enter the following value: com.versa.systemextension. Server Enter your Versa gateway FQDN. For example, acme.poc.versanow.net.

- Click Next, and then define the distribution.
- Click Done.
Approve System Extension
You can prevent system extension blocked prompts from displaying. To do this, approve the Versa SASE system extension in Ivanti Neurons for MDM.
To approve system extension:
- In Ivanti Neurons for MDM, click Configurations > Add.
- Search for and select macOS System Extension.
- In the Name field, enter Versa SASE - System Extension Approval.
- In the Configuration Setup section, enter information for the following fields.

Field Description Allowed System Extensions (Group of fields) Click + Add to activate the fields below. - Allowed Team Identifiers
Enter the following value: 47J4JTFE29. - Allowed System Extensions
Enter the following value: com.versa.systemextension.sslse. Allowed System Extension Types (Group of fields) Click + Add to activate the fields below. - Allowed Team Identifiers
Enter the following value: 47J4JTFE29. - Allowed System Extensions Types
Enter the following value: Network extension. - Click Next.
- In Distribution, select the target macOS device group.
- Click Done.
Configure App Notifications
You can ensure critical security alerts are visible and prevent Allow Notifications prompts from displaying. To do this, you deploy an app notifications configuration for the Versa SASE client.
To configure app notifications:
- In Ivanti Neurons for MDM, click Configurations > Add.
- Search for and select App Notifications.
- In the Name field, enter the following value: macOS - Versa Notifications.
- In the Configuration Setup section, click Add Apps, and then click the Add Manually tab.
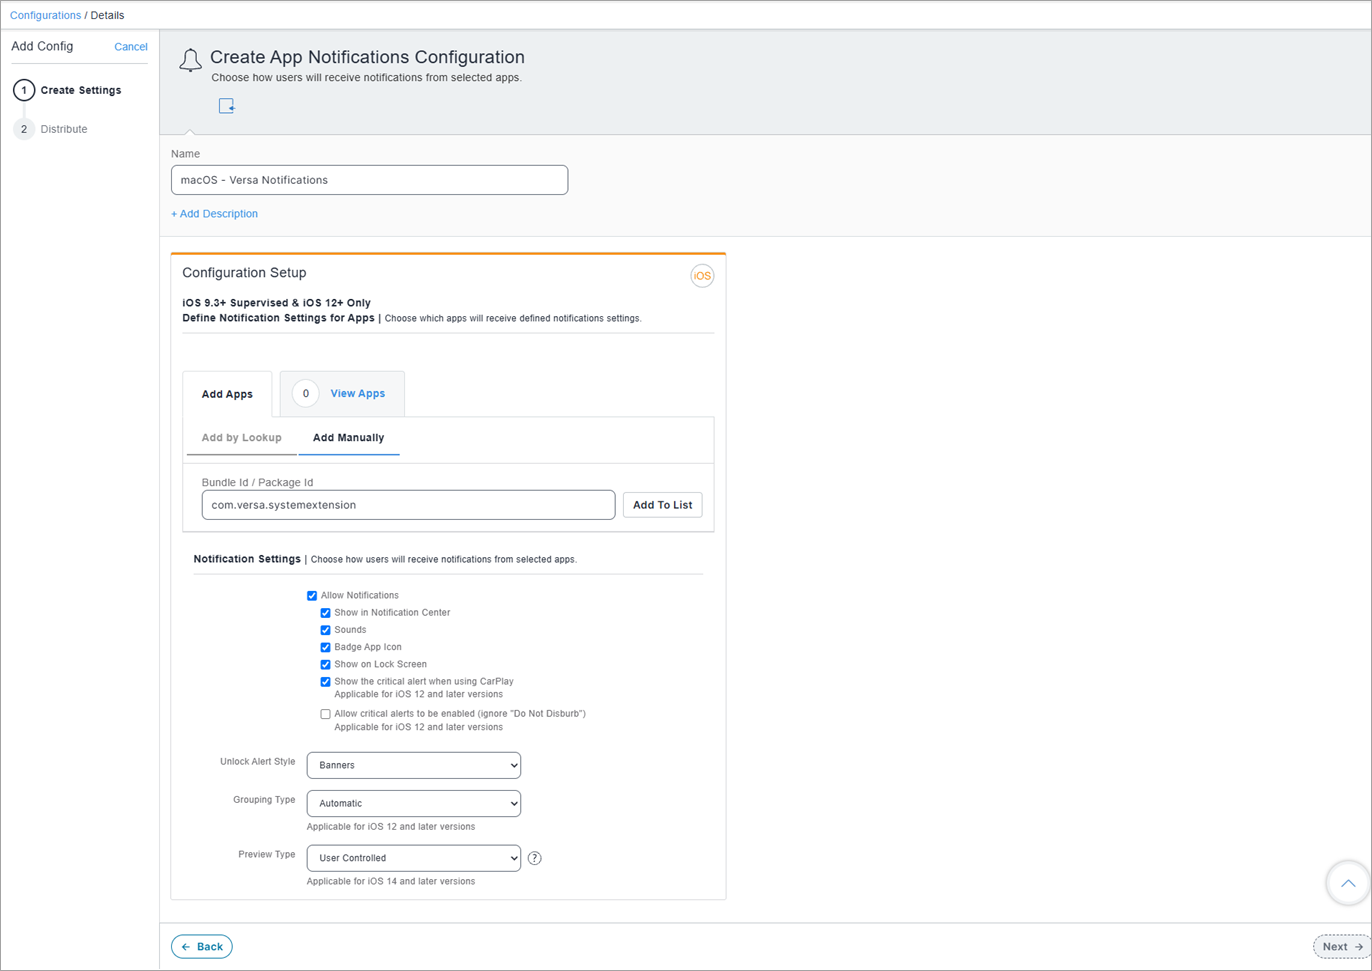
- In the Bundle Id / Package Id field, enter the following value: com.versa.systemextension. Then, click Add To List.
- Repeat the previous step to add com.versa.versasase (required if using the standard GUI app).
- Enter information for the following fields.
Field Description Notification Settings (Group of fields) Select the following options:
- Allow Notifications
- Show in Notification Center
- Sounds
- Badge App Icon
- Show on Lock Screen
- Show the critical alert when using CarPlay
- Unlock Alert Style
Click the drop-down list and select Banners. - Grouping Type
Click the drop-down list and select Automatic. - Preview Type
Click the drop-down list and select User Controlled. - Allow Notifications
- Click Next.
- In Distribution, assign the configuration to your macOS device group.
- Click Done.
Enroll MacOS Devices
To enroll MacOS devices, you must create a distribution in Ivanti Neurons for MDM.
To create a distribution:
- In Ivanti Neurons for MDM, click Apps> App Catalog.
- Click Versa SASE, and then click Distribution.
- Click Edit.
- In Distribution, select the target user group or device group — for example, Everyone.

- Click Save.
- Click Configurations, click your Versa SASE configuration, and then click Edit.
- In Distribution, select the same group used for the application.
- Click Save.
IOS-Specific Deployment Using Ivanti Neurons MDM
This section outlines the steps required to deploy the Versa SASE iOS client (IPA) on iPhone and iPad devices using Ivanti Neurons MDM. The iOS deployment differs from macOS. The app is distributed as an IPA file through the App Catalog, and app configuration is applied as Apple Managed App Configuration, not as a custom profile.
Before you can deploy the Versa SASE iOS client, you need the following:
- IPA file—The iOS application package for Versa SASE.
- Configuration parameters—These can be in a .plist file, or you can use manual key entry.
Create a User and Enroll the Device
- Log in to the Ivanti Admin Portal with your admin credentials.
- Click Users, and then click + Add.

- Fill in the user credentials (username and password). Note these for later steps.

- The enrolled user receives an invitation email from Ivanti with a link to download the MDM enrollment profile. Alternatively, the user can download the Ivanti Go app directly from the App Store.
- On the target iPhone or iPad, open the enrollment link or launch the Ivanti Go app and sign in with the credentials created in Step 3.
- Complete the enrollment process on the device. The device is now managed under Ivanti Neurons MDM.
Upload and Distribute the Versa SASE IOS Application
- Return to the Ivanti Admin Portal.
- Click Apps > App Catalog.

- Click + Add.
- Select In-House to upload the IPA application package.

- Click Choose File and upload the Versa SASE .ipa file.
- Select the appropriate Category for the application and add an optional description.
- Upload screenshots of the application if required.
- Select Do not delegate this app.
- Select Custom and choose Devices / Specific Devices to deploy to selected devices only.

- Under Apple Managed App Configuration, click the + icon.

- Enter a configuration name.
- Upload the configuration parameters using one of the following methods:
- Select Use .plist, click Choose File, and upload your .plist file.
- Alternatively, click Add+ to manually enter each key-value pair. For a list of keys and their corresponding values, see Obtain the Configuration Parameters.
- Click Done.
- Go to Apps > App Catalog, and select the newly-added Versa SASE application.

- Click the three-dot menu and select Send Install/Update Request.
- Select the checkboxes for both Install and Update requests.
- Choose the target devices, and then click Send.

- The enrolled device displays a popup notification prompting the user to install the application.

The following screen displays when you open the application for the first time.

Sample PLIST File for IOS App Configuration
The following is a sample .plist for iOS app configuration:
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>device_id</key>
    <string>${deviceGUID}</string>
    <key>fqdn</key>
    <string>Replace with your portal FQDN</string>
    <key>enterprise_name</key>
    <string>Replace with your Enterprise Name</string>
    <key>user_id</key>
    <string>${userEmailAddress}</string>
    <key>device_name</key>
    <string>${deviceName}</string>
    <key>managed_device</key>
    <true/>
    <key>PayloadRemovalDisallowed</key>
    <true/>
    <key>is_versa_root_ca_required</key>
    <true/>
</dict>
</plist>
Verification
After the deployment policies have run, verify that the onboarding is successful:
- In Ivanti:
- Go to Devices.
- Select a test device, and then click Configurations.
- Confirm that the status displays Applied.
- On the device:
- Open the Versa SASE app.
- Check that auto_logon is set to true, and the FQDN and Username fields are pre-populated. The app may attempt to establish a tunnel immediately.
- In the Versa SASE Tenant Portal:
- Go to Monitor > Remote Access.
- Confirm that the device is listed with the device ID assigned by Ivanti.
Supported Software Information
SASE Client releases 7.6.7 and later support all parameters described in this article, except:
- Release 7.7.1 introduces the macOS parameters listed under Parameters introduced in version 7.7.1 (macOS Only).
- Release 7.7.3 introduces the macOS parameters listed under Parameters introduced in version 7.7.3 (macOS Only).