
Configure NPU Traffic Mirroring
 For supported software information, click here.
Traffic mirroring lets you copy network traffic from an interface and send the traffic to out-of-band security and monitoring appliances for additional processing, including content inspection, threat monitoring, and troubleshooting. Versa Operating SystemTM (VOSTM) devices that use network processing (NPU) switching hardware support traffic mirroring, also known as switched port analyzer (SPAN), in which the SPAN session sends a copy (mirror) of the traffic to another interface on the VOS device.
Encapsulated remote SPAN (ERSPAN) is a type of traffic mirroring in which the mirrored Layer 2 packets can be routed over a Layer 3 IP network. ERSPAN wraps the mirrored packets in IP frames using the Generic Routing Encapsulation (GRE) protocol. This enables mirroring of traffic to a monitoring node located anywhere across the routed network.
This outer frame provides the necessary information (like source and destination IP addresses) for routing the mirrored traffic across the network. The switch finds the outgoing port of the mirrored packets by looking up the destination IP address in its routing table.
Enable a Mirror Interface
To begin configuring NPU traffic mirroring, you first need to enable a mirror interface:
- In Director view, select the Configuration tab in the top menu bar.
- Select Templates > Device Templates in the horizontal submenu bar.
- Click the name of a post-staging template. The view changes to Template view.
- Select Networking > Interfaces in the left menu bar, then click ENet in the horizontal submenu. The following screen displays.

- Click the
 Add icon to create a new ENet interface for NPU mirroring, or select an interface in the main pane to edit an existing ENet interface. The Add/Edit Ethernet Interface popup window displays.
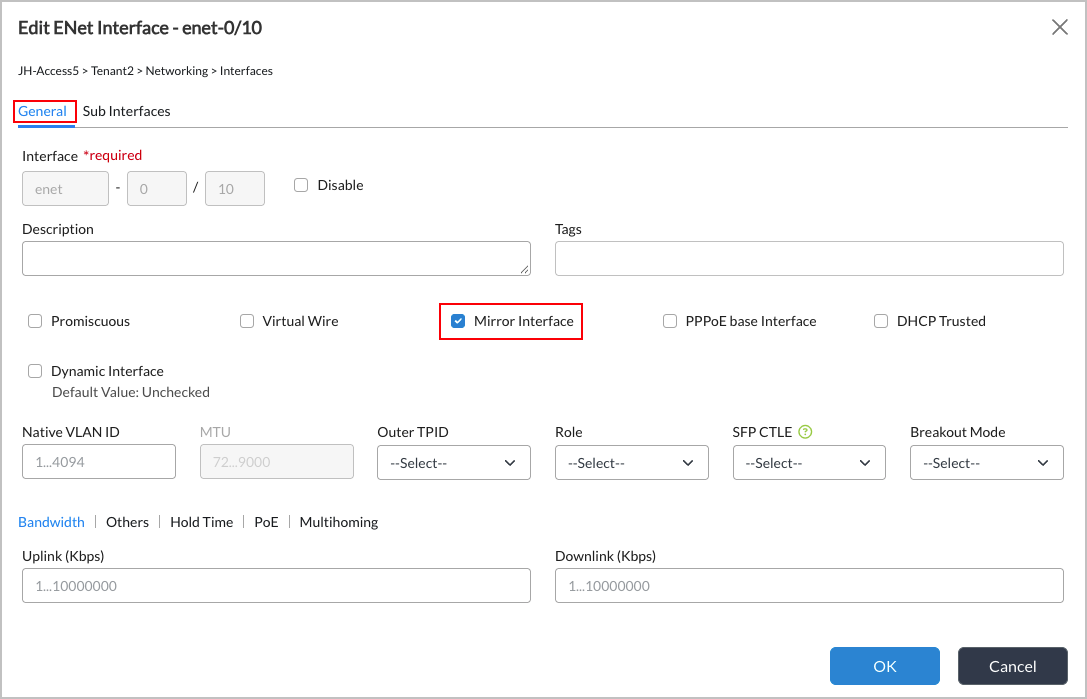
- In the General tab, click the Mirror Interface check box, then click OK.
Note: If you manually create a new interface, you must add the interface to the Traffic Identification list of interfaces under Organization Limits. See Steps 7 and 8 below for more information.
- Select Others > Organization > Limits in the left menu bar, then select an organization in the main pane. You must select an organization whose Appliance Owner field status is True. The Edit Organization Limit popup window displays.

- In the Traffic Identification tab, select the mirror interface you configured above.

Configure SPAN
To configure Switched Port Analyzer (SPAN) to send a copy (mirror) of the traffic to another interface on the VOS device:
- Select Director View in the top menu bar.
- Select Devices > Devices in the horizontal menu bar.
- Click the name of an appliance. The view changes to Appliance view.
- Select the Configuration tab in the top menu bar.
- Select Networking > NPU > Traffic Mirroring in the left menu bar.

- Select the Policies tab in the horizontal menu.
- Click the + Add icon or button. In the Add Policies window, enter information for the following fields.

Field Description Name (Required) Enter a name for the NPU ACL traffic-mirroring policy. Description Enter a text description for the NPU traffic-mirroring policy rule.
- Click OK.
- Select the Rules tab in the horizontal menu bar.
- Click the + Add icon or button. The Add Rules popup window displays.

- Select the General tab, and then enter information for the following fields.
Field Description Name (Required) Enter a name for the NPU ACL traffic mirroring policy. Description Enter a text description for the NPU ACL policy rule. Disable Rule Click to disable the rule when you commit the configuration.
- Select the Match tab, and then enter information for the following fields.

Field Description Match Direction (Group of Fields) - Ingress
Click to have the rule match incoming traffic. - Egress
Click to have the rule match outgoing traffic. - Ingress Egress
Click to have the rule match both incoming and outgoing traffic. Routing Instances (Tab) Select the routing instances to which to apply the rule. - + Add icon
Click to add a new routing instance. The Add Routing Instances popup window displays. - Name
Select the name of the routing instance. - Bridge Domain List
Select the name of the bridge domain within the routing instance. - OK
Click OK to add the new routing instance to the rule. Interfaces (Tab) Select the interfaces to which to apply the rule.The Add Interfaces popup window displays. - Name
Select the name of the interface and interface port to which to apply the rule.
- Select the Set tab, and then enter information for the following fields.
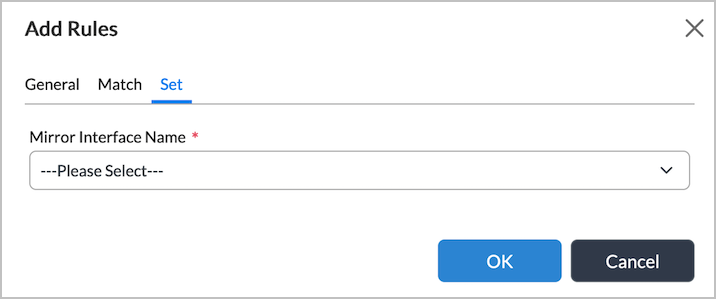
Field Description Mirror Interface Name Select the name of the interface to which to mirror the traffic.
- Click OK.
Configure ERSPAN
Releases 22.1.4 and later.
To configure Encapsulated Remote Switched Port Analyzer (ERSPAN), you create a mirroring profile that defines the source and destination of the mirrored traffic. Then, you create a policy with rules for the traffic that you want to mirror. When you associate the policy with the profile, packets from the source that match the criteria in the rules are mirrored to the destination.
To configure ERSPAN:
- In Director View:
- Select Configuration in the top menu bar.
- Select Devices > Devices in the horizontal menu bar.
- Click the name of an appliance. The view changes to Appliance view.
- Select Networking > NPU > Traffic Mirroring in the left menu bar. The following screen displays.

- Select the Profiles tab in the center pane. The following screen displays.

- Click the + Add icon to create a mirroring profile.
- In the Create Profile window, enter information for the following fields.

Field Description Name Enter a name for the mirroring profile. Type Select ERSPAN. Destination IP Address Enter the destination IP address, which is where you want to send the mirrored traffic. Source IP Address Enter the source IP address of the mirroring device. Routing Instance Enter the destination routing instance.
Default: GlobalDSCP Differentiated Services Code Point (DSCP) value for the traffic you want to mirror.
Default: be
TTL Time to live of the mirrored traffic. Truncate Select to truncate the mirrored traffic. When truncation is enabled, the maximum packet size is 226 bytes.
Default: Disabled.
- Click OK.
- Select the Policies tab in the horizontal menu.
- Click the + Add icon to create policy rules.
- In the Add Policies window, enter information for the following fields.
Field Description Name (Required) Enter a name for the ERSPAN policy. Description Enter a text description for the ERSPAN policy.
- Click OK.
- Select the Rules tab in the center pane.
- Click the + Add icon. The Add Rules window displays.
- Select the General tab, and then enter information for the following fields.
Field Description Name (Required) Enter a name for the rule. Description Enter a text description for the rule. Disable Rule Click to disable the rule when you commit the configuration.
- Select the Match tab, and then enter information for the following fields.
Field Description Match Direction (Group of Fields) - Ingress
Click to have the rule match incoming traffic. - Egress
Click to have the rule match outgoing traffic. - Ingress Egress
Click to have the rule match both incoming and outgoing traffic. Routing Instances (Tab) Select the routing instances to which to apply the rule. - + Add icon
Click to add a new routing instance. The Add Routing Instances popup window displays. - Name
Select the name of the routing instance. - Bridge Domain List
Select the name of the bridge domain within the routing instance. - OK
Click OK to add the new routing instance to the rule. Interfaces (Tab) Select the interfaces to which to apply the rule.The Add Interfaces popup window displays. - Name
Select the name of the interface and interface port to which to apply the rule.
- Select the Set tab, and then select the name of the interface to which to mirror the traffic.
- Click OK.
Supported Software Information
Releases 22.1.1 and later support all content described in this article, except:
- Release 22.1.4 adds support for ERSPAN.